
Secure design principles
Page 8 of 17
Virtualisation security design principles
The principles are a subset of the Cyber security design principles, extending them to help you think through the security considerations when designing systems that use virtualisation.
Virtualisation
Deploying and maintaining discrete systems using physical infrastructure, such as servers and network routers can be expensive, time consuming and inefficient. Virtualisation allows multiple systems to share physical resources, enabling many virtual systems to be created and deployed cheaply and quickly.
Virtualisation is a valuable tool for consolidating resources, supporting legacy systems, increasing flexibility and reducing costs. Although it is often used to build compute resources, it can be applied at many layers of a system, including networking and storage.
This technology is powerful, but it also introduces additional layers of complexity and, potentially, additional risks into your systems. It's therefore important to ensure that security is considered throughout the design process of any system which relies on virtualisation.
These principles aim to help you design systems that take advantage of virtualisation, without also introducing unmanageable risks.
Terminology
There are many different types of virtualisation including compute, networking, storage, with more novel applications being continuously devised. We'll focus on infrastructure virtualisation but these principles could be applied to any type of virtualisation.
Components of a virtual system
Throughout this guidance we refer to virtualised systems, virtual instances and virtualisation platforms.
The diagram and definitions below will help you grasp how these objects are related
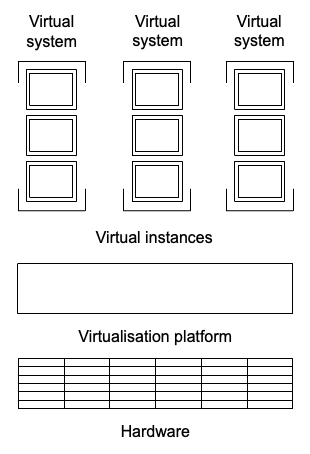
Virtual system – A system built using multiple virtual instances running on the virtualisation platform.
Virtual instance – The logical virtual instance which runs on the virtualisation platform. This could be a full fledged virtual machine, virtual firewall or other networking device, or perhaps a virtual file system. Virtual instance are generally logical representations of physical resources, but may also be an additional layer of abstraction, used to bring multiple resources into a single logical view.
Virtualisation platform – The underlying provider of virtualisation. The platform allows multiple, segmented virtual instances to be run on it and manages the resources that are available to them. The virtualisation platform can include many components such as the hypervisor, orchestration and management functions.
Hardware – The physical hardware that the virtualisation platform runs on. Often hardware has specific features to enable efficient virtualisation so that the hardware can be shared between virtual instances at near native speed.
Audience
The primary audiences for this guidance are system architects, engineers and security experts designing and building systems using virtualisation.
The principles may also be useful for review and accreditation activities.
Structure of virtualisation security principles
These principles will guide you through some of the risks associated with virtualisation and provide guidance on mitigating those risks. You will gain the most from these principles if you use them to guide your security choices early in your project's design process.
We've split the principles into five sections, each dealing with a specific aspect of system security: