Building a Security Operations Centre (SOC)
Page 9 of 14
Detection
Detections, analytics, and use cases are some of the terms used to describe a SOCs approach to detection of attacks. These terms can vary, as can the approach taken.
Here, we will expand on the approaches outlined in the Operating Model section, exploring the key differences, while remaining technology agnostic.
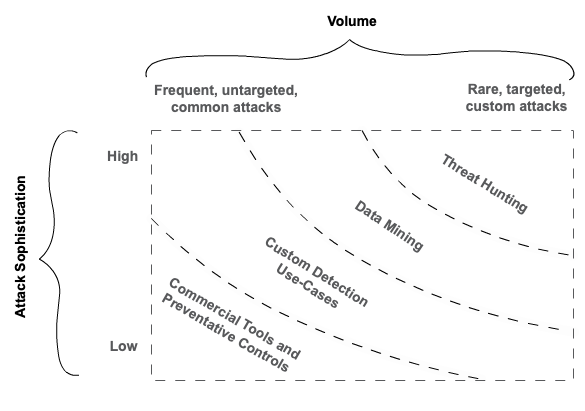
The diagram below characterises the capability of a SOC according to attack(er) sophistication and the volume of attacks that are likely to be realised. It demonstrates that the majority of low sophistication, high volume/frequency attacks should by handled by commercial tools and preventative controls.
Conversely, if your threat profile includes highly sophisticated, targeted attacks, you will likely need to employ some suitably capable individuals to tackle the problem.