
Cyber Security Toolkit for Boards
Resources to help Boards implement the actions outlined in the Cyber Governance Code of Practice.
Page 18 of 27
Understanding the cyber security threat
Threat intelligence is key for organisations looking to build cyber resilience.
Introduction
Understanding the threats faced by your organisation will enable you to tailor your organisation’s approach to cyber security investment accordingly. You need to prioritise what threats you are trying to defend against, otherwise you risk trying to defend against everything, and doing so ineffectively.
The benefits of building your understanding of the cyber security threat include:
- Organisations that are routinely gathering information from reliable sources are able to respond rapidly and appropriately to new and emerging threats.
- Knowing how you are exposed to cyber security threats will help your security team to focus their attention on the most important areas, and use your resources as efficiently as possible.
- A thorough understanding of different threats will help an organisation clearly communicate the rationales for security measures to staff, leading to a better degree of compliance.
- Robust risk management as the threats are understood and managed. This can be particularly important during periods of transition, for instance when preparing for a merger with a company which may be exposed to a different level or type of threat.
Essential activities
Understand the cyber security threat landscape
The board should have an awareness of the wider threat landscape through a regular threat briefing. This should include current threats which could affect all organisations and those that are specific to the business. Changes in the threat position should be included in the management information that the board receives at its board meeting. Sign up to the NCSC’s threat reports and advisories on cyber security matters affecting the UK.
Build your threat assessment into your risk management
Ensure that your organisation carries out regular threat assessment exercises to identify who might attack your organisation, their capabilities and motivations. This should involve suppliers and partners as many organisations have close dependencies on external parties for critical assets or as part of a supply chain. The outputs of the threat assessment should feed into the risk management process, and unacceptable risks should be escalated to the board.
Consider threat intelligence
You should consider acquiring deeper level of threat intelligence, especially if you’re a larger organisation dealing with critical infrastructure. For instance, organisations operating a Security Operations Centre (SOC) will typically make use of finer-grained information, via the NCSC, commercial providers, or open source, about indicators of compromise and the tactics and techniques in use by adversaries.
Collaborate on security
The people responsible for cyber security in your organisation should participate in collaborative information sharing forums with sector peers. Attackers often target a number of organisations in the same sector in a similar manner.
Traffic Light Protocol (TLP)
Collaborating with your competitors may seem counter-intuitive, but there is a precedent and well-established process for sharing information in a way that protects commercially sensitive information, known as the Traffic Light Protocol (TLP). It is used to allocate a sensitivity category to information. There are four information sharing levels: RED, AMBER, GREEN and CLEAR.
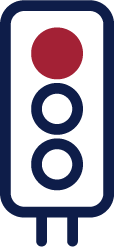 RED | RED Non-disclosable information, restricted to representatives present at the meeting. Representatives must not further disseminate the information. RED information may be discussed during a meeting, provided all representatives present have signed up to these rules. Guests and others such as visiting speakers who are not full members will be required to leave before such information is discussed.
|
|---|---|
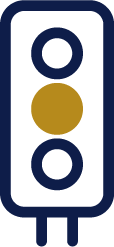
AMBER | AMBER Limited disclosure and restricted to members of the forum and those within their organisation (whether direct employees, consultants, contractors or outsourced staff working in the organisation) who have a need to know in order to take action.
|
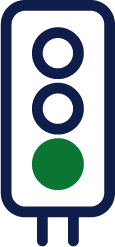
GREEN | GREEN Information can be shared with other organisations, or individuals in the cyber security community, but not published or posted on the internet.
|
CLEAR | CLEAR Information that is for public, unrestricted dissemination, publication, web posting, or broadcast. Any member may publish the information, subject to copyright.
|
Note: Ensuring that collaboration between competitors is continuous is likely to require board-level support.


