New online training helps board members to govern cyber risk
Effective cyber governance starts at the top.
This means board members have a critical role in ensuring their organisations are able to exploit the opportunities that technology brings in such a way that they build a resilient and secure business.
The vast majority of modern businesses rely on information, data and digital technology to function. This means that cyber security risk - like financial and legal risk - needs to be on the Board’s agenda.
Throughout my career, I’ve seen firsthand how cyber security is essential for driving growth, strengthening resilience, and ensuring long-term success. This is now happening against a backdrop where increasingly complex supply chains make it more challenging to understand the cyber risk to a company’s operations, and therefore more critical to govern cyber risk effectively.
The NCSC, working with our colleagues in the Department for Science, Innovation and Technology (DSIT), Non-Executive Directors (NEDs) and industry experts, has produced a package of resources to help boards meet the imperative to govern cyber security risks. This is because ultimately, cyber security is a board-level responsibility.
We also worked closely with NEDonBoard who have helped ensure that the content is both practical and relevant for boards.
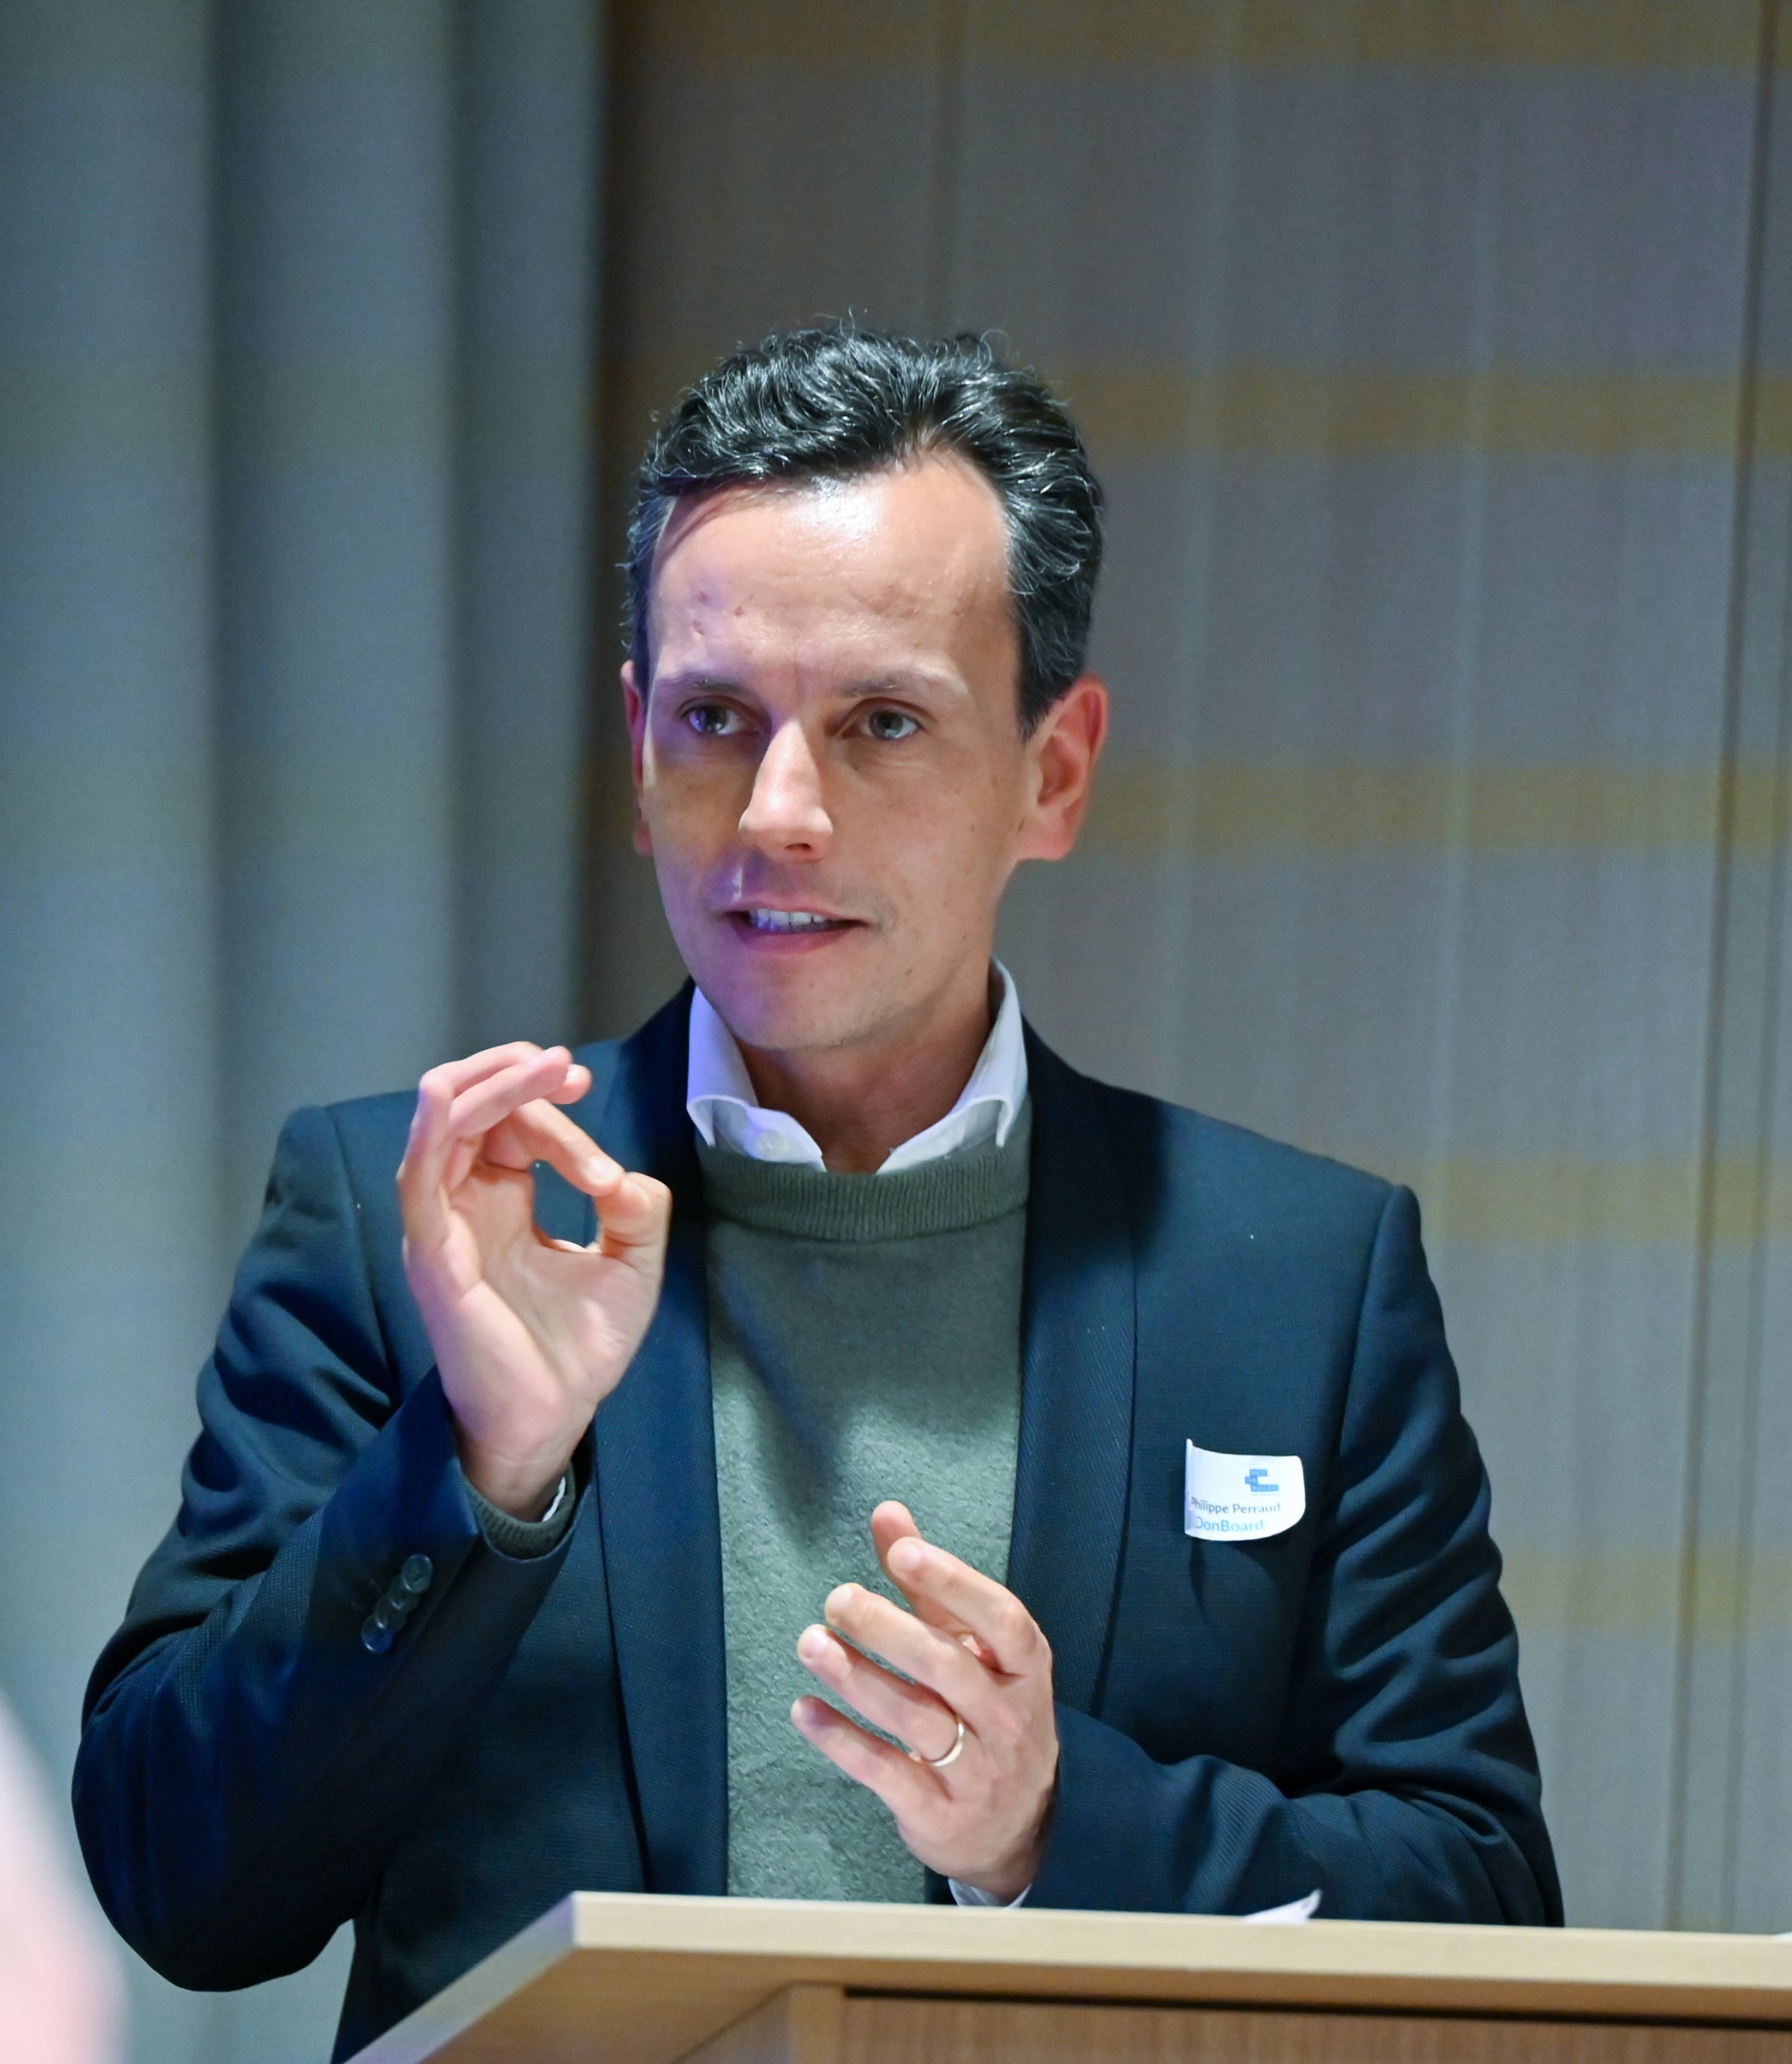
Jean-Philippe Perraud, the founder and CEO of NEDonBoard, said:
 |
|
The cyber resources and NCSC’s training provide essential guidance, and we encourage all boards to prioritise cyber security. NEDonBoard is delighted to have contributed to shaping these vital tools for board leadership.
The new resources include:
- The Cyber Governance Code of Practice describes what actions boards must take to ensure cyber risks are managed effectively in their organisation.
- The Cyber Governance Training explains why those actions are important, and how to implement them in a practical, actionable way.
- The Cyber Security Toolkit for Boards provides boards with the in-depth resources to support cyber risk governance.
The Cyber Governance Training aligns with the five core principles from the Cyber Governance Code of Practice. These are:
- Risk Management
- Strategy
- People
- Incident Planning, Response & Recovery
- Assurance & Oversight
Each module takes around 20 minutes to complete, and includes expected learning outcomes and links to relevant NCSC resources.
I’d encourage all board members to use these resources to help them embed cyber security into their board’s governance. From my experience of working with senior leaders across private and public sectors, I know that strong cyber governance is key to resilience, growth, and long-term success. Board members play a vital role in making this happen.
We’re always looking to improve our guidance, if you have any feedback you can get in touch by emailing [email protected]. We'll be happy to hear from you.