
Guidance
How to assess and gain confidence in your supply chain cyber security
Practical steps to help medium to large organisations gain assurance about the cyber security of their organisation's supply chain.
Page 3 of 29
Executive summary
The guidance is broken into 5 stages, with key steps in each stage. These are summarised in the following diagram. Note that some of the steps in stages 3 and 4 (Monitor supplier security performance and Report progress to the board) can be carried out in parallel.
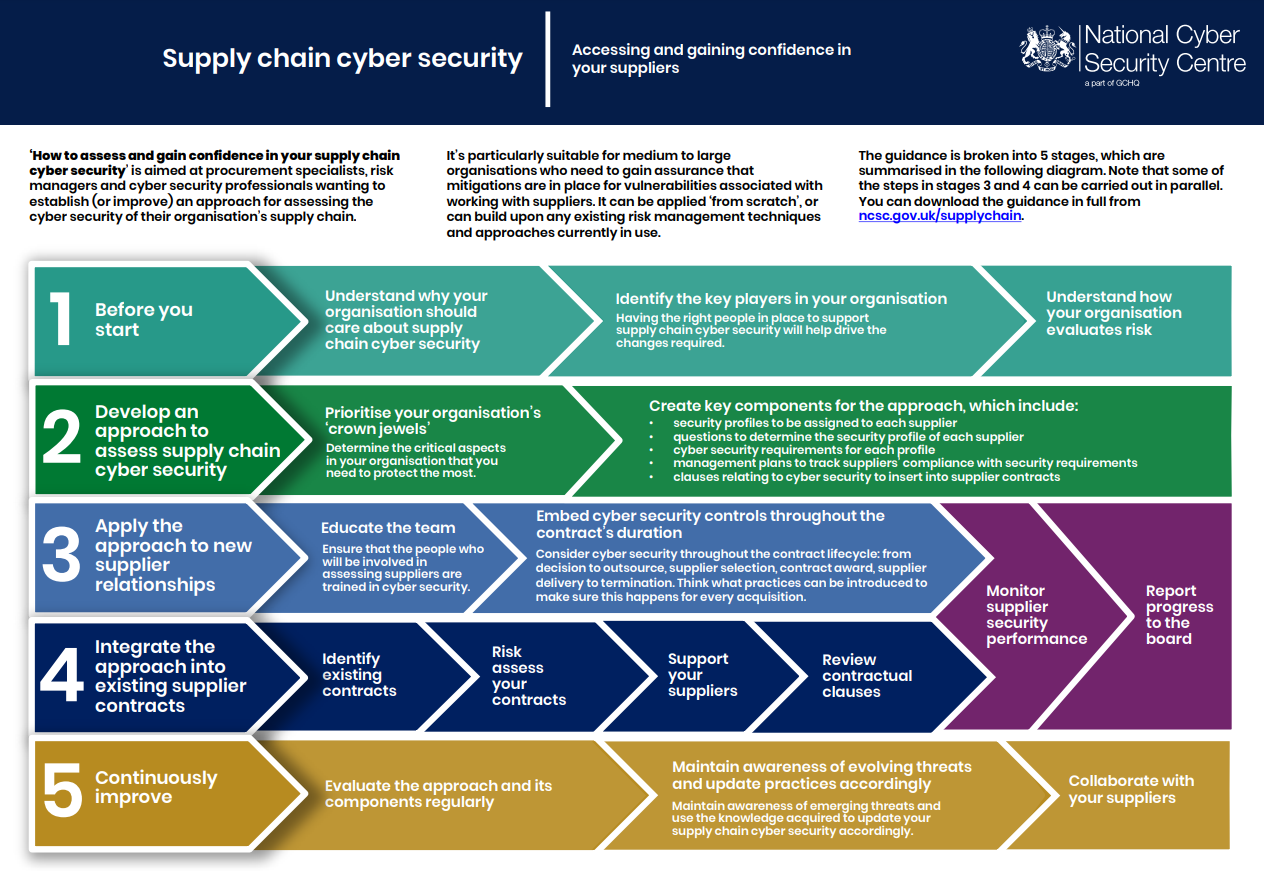
There is a pdf of the Supply chain cyber security summary and the individual stages which can be downloaded using the link or available from the Downloads section of the title page in this guidance collection.