
Recognising UK-based security researchers who have disclosed vulnerabilities to UK government
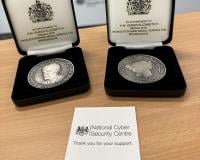
On Friday 1 March, we hosted a special event at our NCSC headquarters in London for some of the UK-based vulnerability researchers who have contributed to vulnerability disclosure programmes across government. It was a great opportunity to meet them in person, show our appreciation and learn from their expertise.
The highlight of the event was the presentation of our NCSC Challenge Coins, which are awarded to researchers who have shown themselves to be exemplars of the vulnerability disclosure community. The coins are a symbol of our gratitude and recognition for their valuable work in helping us protect the UK from cyber threats. The NCSC CTO, Ollie Whitehouse and Cabinet Office Deputy Director for Cyber Policy and Capabilities, Michael Brunton-Spall, joined us to present the coins and personally thank the recipients.
Ollie said
“It was great to meet with members of the UK-based researcher community and an honour to award them their coins. We want all security researchers, regardless of where they are in their career, to feel empowered to be able to responsibly discover and report vulnerabilities without negative repercussions and ultimately feel safe to hold a mirror up to Government to help keep us honest. National security is a team sport, and we are deeply grateful for their efforts in our collective mission to make the UK the safest place to live and work online.”
Michael spoke with the researchers about the new Government Cyber Coordination Centre (GC3) which at its heart is a community initiative, bringing together cyber defenders across government enabling UK government to improve its cyber resilience and “Defend as One”. Members of the public responsibly disclosing vulnerabilities to government through the Vulnerability Reporting Service and Disclosure for Government Schemes are helping towards that goal.
After the presentation, there was a series of talks from researchers who shared their insights and experiences on finding and reporting vulnerabilities. Their thoughts about how to improve security posture and best practices were shared with UK government departments who were also there. The researchers' skills and knowledge was really evident, and a lot was learnt from their presentations.
We also had representatives from our partners HackerOne and NCC Group who have been instrumental in supporting our vulnerability disclosure programmes, facilitating communication with the researchers since 2018.
The event was a huge success and we are very grateful to everyone who took part – and not forgetting the international researchers who have already received their coins.
We hope this event will inspire more researchers to responsibly disclose vulnerabilities and help make the UK the safest place to live and work online.
For more about vulnerability management, the NCSC’s recently updated guidance is available, which also includes advice on vulnerability disclosure.


