
NCSC CEO and Information Commissioner sign Memorandum of Understanding
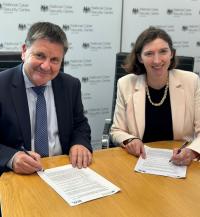
The Chief Executive of the National Cyber Security Centre, Lindy Cameron, and the Information Commissioner, John Edwards, have today signed a joint Memorandum of Understanding (MoU) that sets out how both organisations will cooperate.
The MoU recognises that whilst both organisations have distinct responsibilities, there are opportunities to align work on some shared issues and deconflict on others.
These include cooperation on the development of cyber security standards and guidance as well as influencing improvements in the cyber security of organisations regulated by the Information Commissioner’s Office (ICO).
The MoU reaffirms that the NCSC will never pass information shared with it in confidence by an organisation to the ICO without having first sought the consent of that organisation.
NCSC CEO Lindy Cameron said:
“This new MoU with the Information Commissioner builds on our existing relationship and will boost the UK’s digital security.
“It provides us with a platform and mechanism to improve cyber security standards across the board while respecting each other’s remits.”
Information Commissioner John Edwards said:
“We already work closely with the NCSC to offer the right tools, advice and support to businesses and organisations on how to improve their cyber security and stay secure.
“This Memorandum of Understanding reaffirms our commitment to improve the UK's cyber resilience so people's information is kept safe online from cyber attacks.”
Key provisions in the new MoU include:
- The Commissioner will encourage organisations to engage appropriately with the NCSC on cyber security matters, including the response to cyber incidents.
- The Commissioner will also incentivise engagement with the NCSC, including recognising organisations affected by significant cyber incidents that report to and work with the NCSC. The ICO also commits to exploring how it can transparently demonstrate that meaningful engagement with the NCSC will reduce regulatory penalties.
- The ICO will support the NCSC’s visibility of UK cyber attacks by sharing information with NCSC about cyber incidents, on an anonymised and aggregate basis, as well as incident specific details where the matter is of national significance. Doing so will help NCSC make the UK the safest place to live and work online, ensure its advice and guidance remains fit for purpose, and that NCSC services keep pace with the evolving threat landscape.
- Where NCSC and ICO are both engaged on a cyber incident, they will endeavour to deconflict to minimise disruption to an organisation’s efforts to contain and mitigate harm. In doing so, the Commissioner will seek to enable organisations to prioritise engagement with the NCSC and their partners in the immediate aftermath where that will prioritise mitigative work.
- NCSC and ICO will provide each other with ongoing feedback with a view to continuous improvement in relation to their collaboration.
- The NCSC and ICO will work together to enhance cyber security guidance available and encourage its adoption.